TL;DR
The newly reported Pass-ta-key attack has generated concern but is largely considered a low-risk vulnerability by security experts. Its practical impact appears minimal, and many details remain uncertain.
Security researchers have identified a new vulnerability dubbed the Pass-ta-key attack, but cybersecurity experts say its practical impact is limited, and it is unlikely to pose a widespread threat.
The Pass-ta-key attack was publicly disclosed after researchers demonstrated a method to exploit certain vulnerabilities in specific authentication systems. However, leading security analysts, including those from cybersecurity firms and academic institutions, have stated that the attack requires very specific conditions to succeed and is unlikely to be used in real-world scenarios.
Initial reports suggested that the attack could potentially bypass some forms of two-factor authentication or key-based security measures. Yet, experts emphasize that the attack’s effectiveness depends heavily on the implementation details of the targeted systems, which vary widely. Furthermore, many affected systems have already issued patches or updates to mitigate the threat.
Limited Practical Risk of the Pass-ta-key Attack
This development is significant because it highlights how initial concerns about new vulnerabilities can sometimes be overstated. While the Pass-ta-key attack demonstrates a theoretical flaw, cybersecurity professionals agree that its real-world exploitation is unlikely to cause widespread damage. This reassures users and organizations that current security measures remain robust against this specific threat.

Yubico – Security Key C NFC – Basic Compatibility – Multi-Factor authentication (MFA) Security Key and passkey, Connect via USB-C or NFC, FIDO Certified
- Security Protection: Protects against phishing attacks
- Wide Compatibility: Works with 1000+ accounts including Google, Microsoft, Apple
- Easy Authentication: Fast login via USB-C or NFC tap
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Background and Initial Concerns Over Pass-ta-key
The Pass-ta-key attack was first reported by independent security researchers who demonstrated how certain authentication tokens could be compromised under specific conditions. The vulnerability was initially perceived as potentially serious because it could, in theory, allow attackers to bypass some forms of key-based security. Following the disclosure, many organizations and security vendors issued advisories and patches to address the concern. However, subsequent analysis from experts suggests that the attack’s practical application is limited, requiring very specific system configurations and conditions.
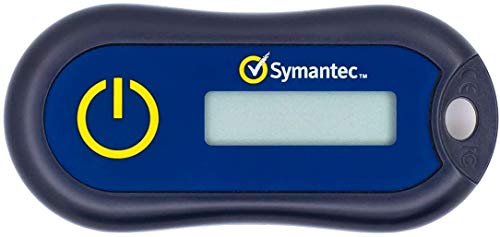
Symantec VIP Hardware Authenticator – OTP One Time Password Display Token – Two Factor Authentication – Time Based TOTP – Key Chain Size
- Compliance: Standard OATH TOTP compliant
- OTP Code: 6-digit code with countdown
- Zero Footprint: No software installation needed
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Unclear How Many Systems Are Truly Vulnerable
It remains unclear how many real-world systems are vulnerable to the Pass-ta-key attack, as the attack requires very specific configurations. Security researchers say that widespread exploitation is unlikely, but some older or poorly maintained systems could still be at risk. Ongoing investigations are assessing the scope of affected devices and systems.
As an affiliate, we earn on qualifying purchases.
Monitoring and Patching Will Continue, Experts Say
Security firms and organizations will continue to monitor for any active exploitation of the Pass-ta-key attack. Developers are expected to release further updates and patches to close potential vulnerabilities. Experts advise users to keep their systems updated and follow security advisories, but overall, the threat level remains low.
As an affiliate, we earn on qualifying purchases.
Key Questions
Is the Pass-ta-key attack a major security threat?
Currently, security experts agree that the Pass-ta-key attack poses limited practical risk and is unlikely to cause widespread harm. It is mostly a theoretical vulnerability that requires very specific conditions to exploit.
Should users be worried about their systems being vulnerable?
Most users and organizations are protected if they keep their systems updated. Patches and security updates addressing the vulnerability have been issued by many vendors.
Will there be more developments regarding this attack?
Security researchers will continue to monitor for any active exploitation and assess the scope of affected systems. Further updates or patches may be released if new risks are identified.
How can organizations protect themselves from this vulnerability?
Organizations should ensure their systems are updated with the latest security patches and follow best practices for key management and authentication security.
Is this attack similar to previous key-exploitation vulnerabilities?
While it shares some conceptual similarities, the Pass-ta-key attack is unique in its specific technical approach and the narrow conditions needed for exploitation. Its practical impact is considered much less severe than past widespread vulnerabilities.
Source: rss